Technology
- Home
- Technology
- News
Notepad++ updates got hijacked for months and could have spied for China
Users of the text and code editor Notepad++ may have unknowingly downloaded a malicious update for the app after its shared hosting servers were hijacked last year. On Monday, the app's developer, Don Ho, posted an update on the attack with more details, incl…
Published 7 months ago on Feb 7th 2026, 5:00 am
By Web Desk

Users of the text and code editor Notepad++ may have unknowingly downloaded a malicious update for the app after its shared hosting servers were hijacked last year. On Monday, the app’s developer, Don Ho, posted an update on the attack with more details, including that the hackers were “likely a Chinese state-sponsored group” and that the app’s servers were vulnerable for roughly six months from June through December 2nd, 2025.
The post explains that the hijacking occurred on the app’s unnamed, now-former hosting provider’s end, stating that “Traffic from certain targeted users was selectively redirected to attacker-controlled served malicious update manifests.” When victims were redirected, their app update could be replaced with a malicious executable that, according to independent cybersecurity expert Kevin Beaumont, may have given the hackers remote access to a victim’s keyboard.
Don Ho’s post also adds that the attack involved “highly selective targeting” in terms of the victims it redirected away from the legitimate Notepad++ website. Kevin Beaumont noted that the victims he spoke with “are [organizations] with interests in East Asia.” So, while this is a serious security vulnerability, it’s possible that the hackers were busy watching specific people instead of just anyone.
The developer did not specify when they became aware of the attack, but said that “all attacker access was definitively terminated” by December 2nd. The Notepad++ updater has been updated itself with stronger security measures to check for tampering and verify that updates are legitimate.
Notepad++ users should make sure they are on at least version 8.8.9, which addressed the vulnerabilities from the hijacking attack, and they should probably download that version directly from the Notepad++ website. Additionally, Kevin Beaumont suggested users double-check that they’re not using an unofficial version of Notepad++, keep a close eye on activity from “gup.exe,” the app’s updater, and check for a suspicious “update.exe” or “AutoUpdater.exe” file in their TEMP folder.
Notably, Don Ho, the developer of Notepad++, criticized the Chinese government in a 2019 app update. He called that version the “Free Uyghur” edition, and told The Verge at the time that his website had faced DDoS attacks in response.
The data centers are winning
- 19 hours ago
Lenovo’s 2-in-1 Yoga 7i is a great Labor Day deal at $750
- 12 hours ago
Death anniversary of renowned TV, film actor Abid Ali observed today
- 10 hours ago
Can synthetic cells save the world?
- 19 hours ago
US military says it destroyed three Iranian oil tankers
- 6 hours ago
OpenAI delayed its new model’s development after the Hugging Face hack
- 12 hours ago
How to train like an Olympic weightlifter
- 19 hours ago
Naqvi backs new administrative units, says Punjab and Sindh identities will remain intact
- 6 hours ago
Dera Ismail Khan range sees improved law and order
- 5 hours ago
The moderates’ plan to slow Hasan Piker has already worked
- 19 hours ago
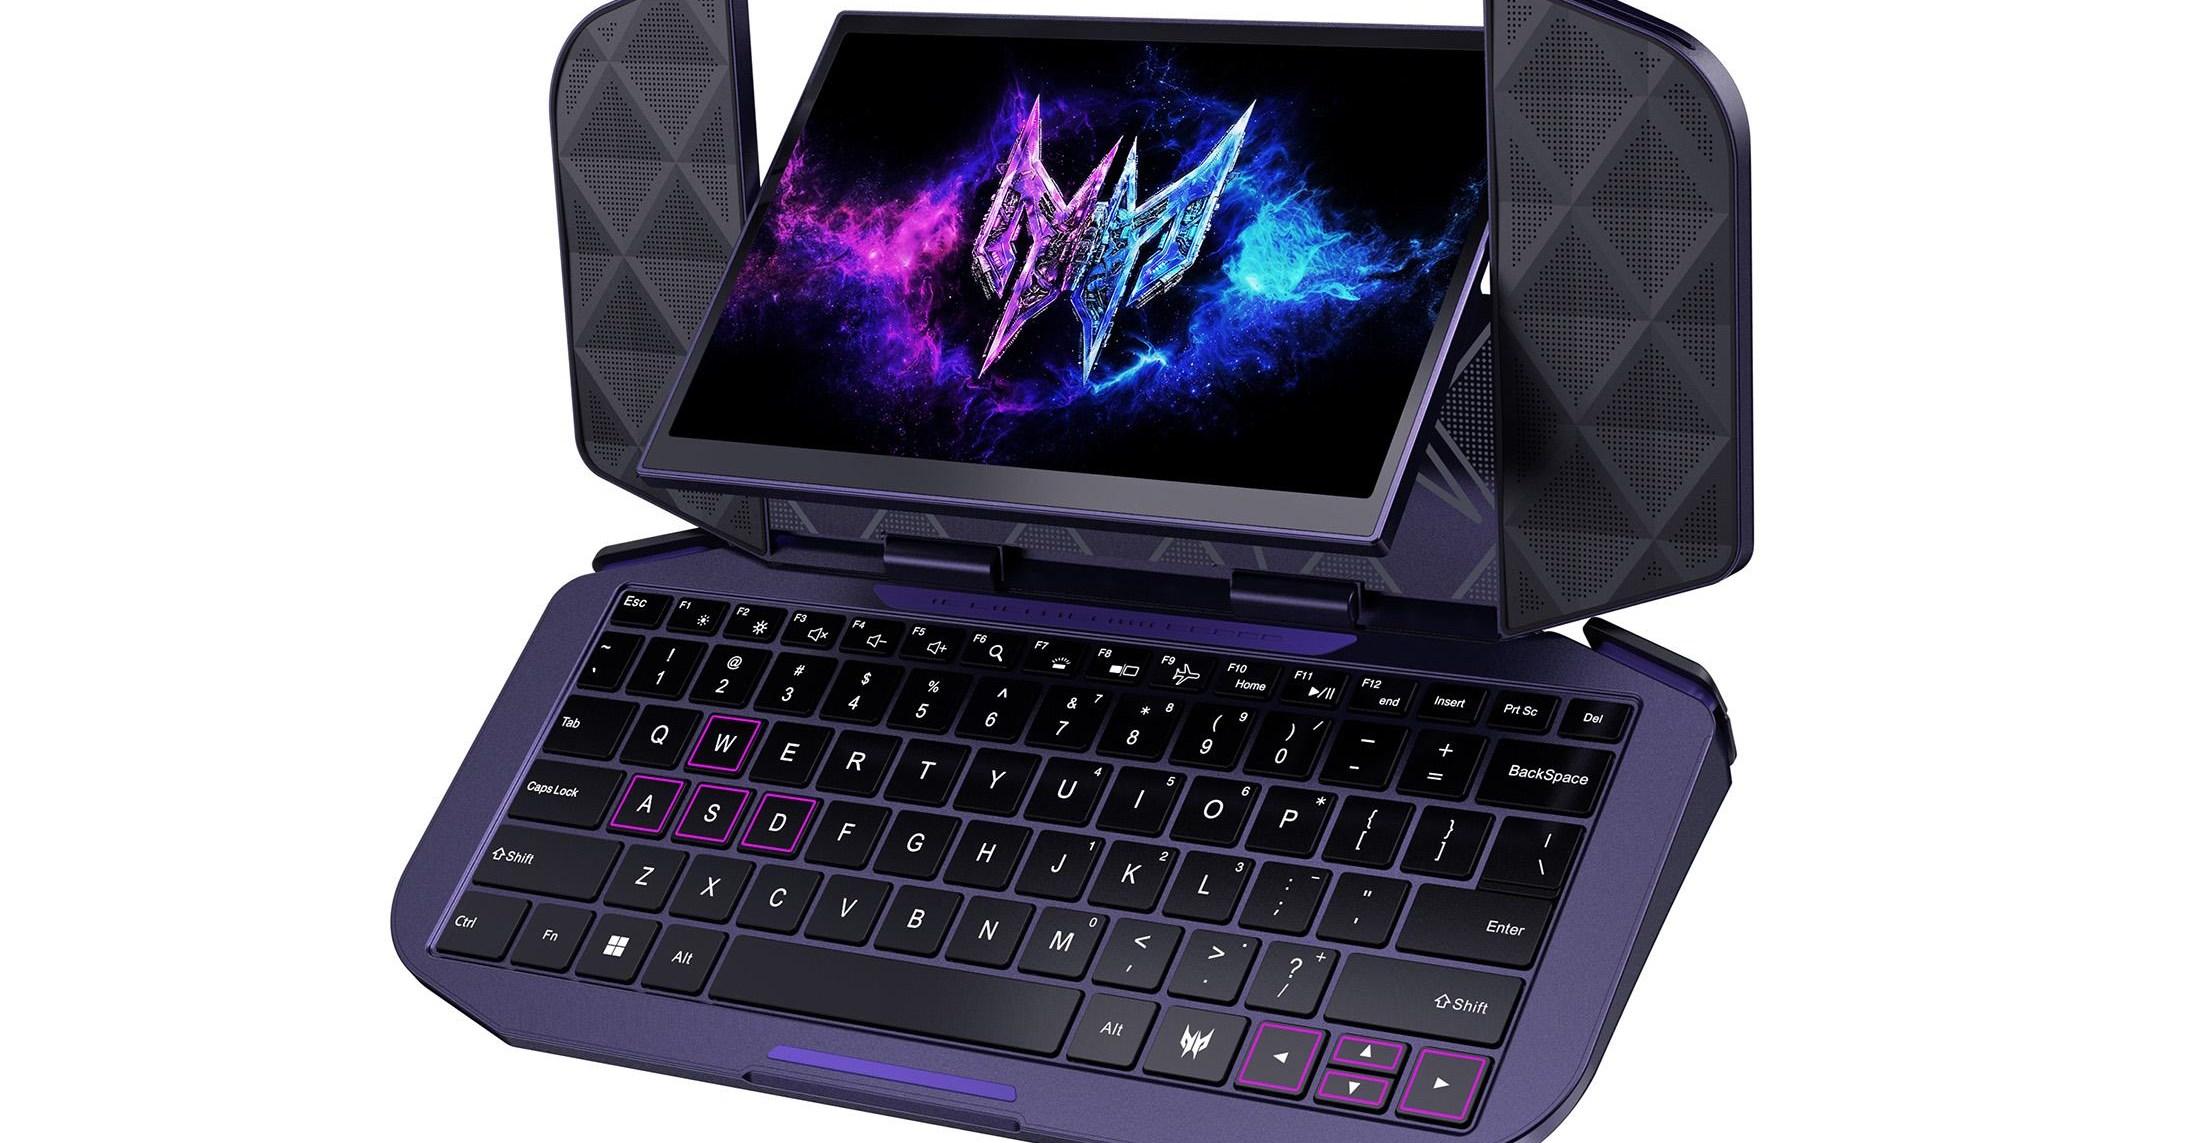
Acer’s new concept hardware is a gaming handheld with a keyboard
- 12 hours ago
Explosions heard near Iran's Kharg Island in Gulf, origin unknown, Fars news says
- 10 hours ago
You May Like
Trending